An enterprise customer is ready to proceed: your software product has passed the technical evaluation and pricing discussions are complete. Procurement then requests your latest SOC 2 report. You have nothing to send.
Australian SaaS companies entering larger markets face an immediate challenge in this situation. Security assurance takes time, and rushing into the wrong assessment may not satisfy the customer’s requirements. Understanding what the buyer expects, and planning backward from the deadline, is where the solution begins.
A calm first step is to find out exactly what was asked for, and by when. The request can leave more room than it first appears to, so ask before you assume.
Which SOC 2 Report Does the Customer Need?
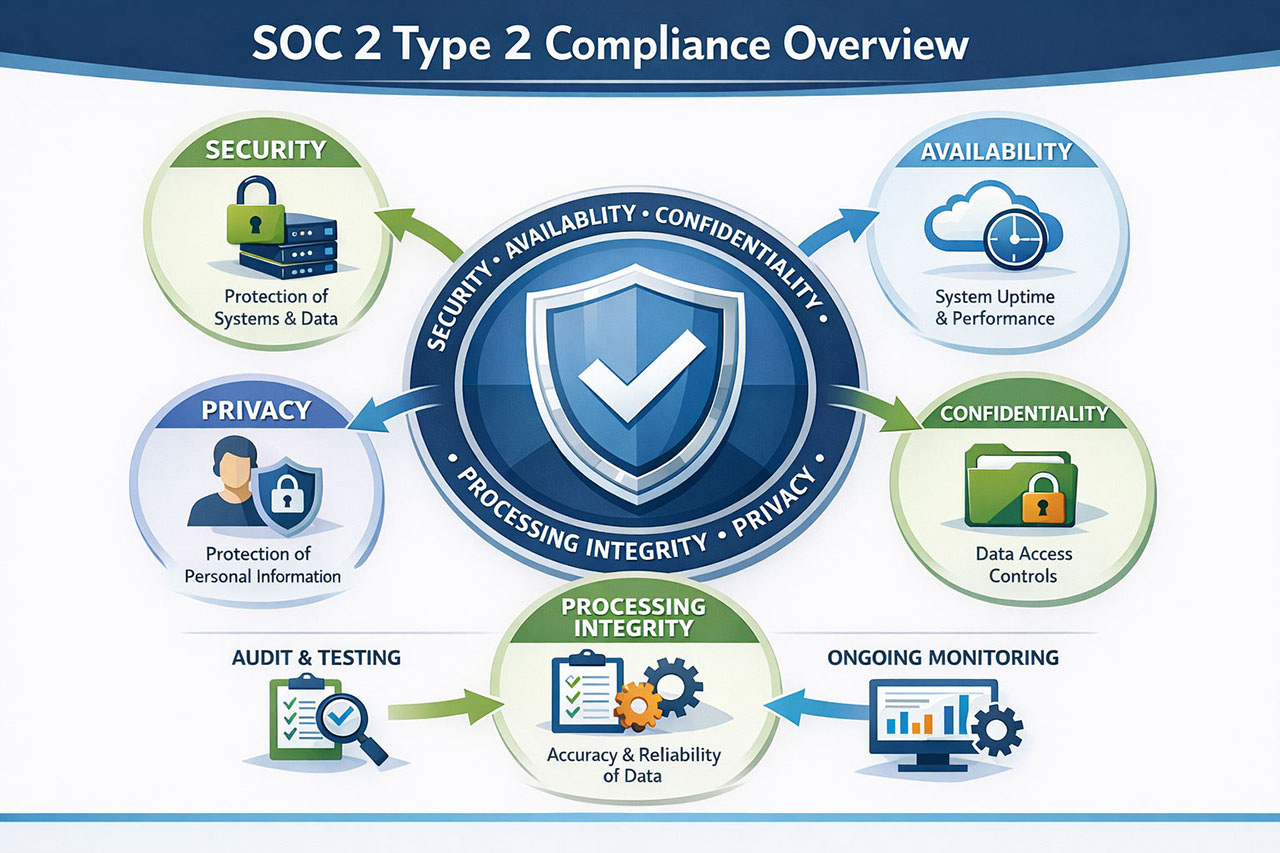
The level of assurance isn’t the same across every SOC 2 report. When responding to enterprise security requirements, the distinction between SOC 2 type 1 vs type 2 matters. Whether relevant controls are suitably designed at a particular date is what Type 1 evaluates. Over a defined period, Type 2 examines both their design and their operating effectiveness.
Some enterprise buyers accept Type 1 for a time, yet many ask specifically for Type 2 because it provides evidence covering actual operations. Confirm the report type, required scope, and acceptable reporting dates with the customer before commissioning an examination.
Put the answers in writing; the report type, scope, and dates all shape the plan and the budget. If the customer’s requirements are unclear, ask for the exact wording in the contract or the security questionnaire.
Let the Observation Period Drive Your Timeline
A SOC 2 type 2 examination cannot be completed simply by preparing documentation and scheduling an auditor. The relevant controls have to be in operation across the whole reporting period. That period may cover three months for an initial examination, while subsequent reports commonly examine longer periods.
Those activities must occur and be documented during the applicable window if your business needs to demonstrate access reviews, security training, or change approvals. By planning backward from a customer deadline, you can see whether the requested report can realistically be delivered on time.
If the deadline is tighter than the observation period allows, tell the customer early. Interim steps, such as a dated plan, are something some customers will discuss if they hear about the gap early.
Understand What the Examination Delivers
Many businesses search for SOC 2 type 2 certification, yet SOC 2 does not issue certificates.
A licensed CPA firm performs an independent examination against the applicable AICPA Trust Services Criteria and issues an attestation report. The assessed system, relevant controls, testing procedures, and the auditor’s opinion are all described in the report.
Customers typically review that document, often under a confidentiality agreement. A SOC type 2 report, too, relates to a specific period in the past. It does not automatically provide assurance about every change made afterward.
Count the Costs Before You Start
More than an independent examination fee is involved in SOC 2 preparation. Businesses may need assistance developing policies, conducting risk assessments, preparing evidence, training employees, and arranging security testing.
Siege Cyber advertises a SOC 2 compliance package priced at AUD $2,750 per month, excluding GST, over twelve months for businesses with up to 50 employees. The advertised offer applies to eligible contracts that are signed by December 31, 2026. The package includes compliance preparation, training, a compliance platform, and external penetration testing.
Siege Cyber indicates typical fees of approximately AUD 5,000–15,000 for the independent CPA examination, which is billed separately, depending on scope and complexity. Make sure you confirm current pricing, eligibility, and deliverables before committing.
What if Your Existing Report Is Out of Date?
Your Type 2 report might cover January through June, and then a customer requests assurance in October. The report does not examine the intervening months. Some customers may accept a management-issued bridge letter describing relevant changes since the reporting period ended.
However, acceptance depends on the customer’s requirements, and a bridge letter does not replace an independent examination. Discuss reporting gaps early rather than assuming an older report will satisfy procurement.
Make Compliance Count Beyond the Next Contract
With fixed-price consulting packages and independent audit coordination, Siege Cyber provides Australian-based SOC 2 readiness support. Growing software companies get the most from connecting compliance preparation with actual operational responsibilities.
Give each control an owner, keep security records, and set a reporting schedule that supports future customer reviews. A successful SOC 2 project prepares your business for the next enterprise opportunity as well as answering the current request.
The next audit cycle is less of a scramble when the evidence you collect has been kept organized from the start. Reviewing responsibilities and schedules at regular intervals helps controls keep operating between audits.